Nightly Security Review Solution
Autonomous AI-Powered Multi-Cloud Security Intelligence & IaC Synthesis Engine
The Problem & Value Proposition
Hyperscale cloud providers release dozens of feature updates, architecture upgrades, and new services every week. For Cloud Security Directors, Enterprise Architects, and DevSecOps teams, keeping up presents significant operational challenges:
- Velocity vs. Governance: Developers adopt new cloud capabilities immediately, often before security teams have established baseline configurations, IAM policies, or encryption requirements.
- Manual Documentation Bottlenecks: Manually reviewing release notes and authoring security guidance takes hours every day.
- Infrastructure as Code Lag: Teams struggle to determine whether a new feature is supported in current Terraform or CloudFormation providers and how to configure it securely.
The Solution: The Nightly Security Review engine solves this by operating as an automated security analyst and IaC generator. Every night, it ingests official cloud feeds, evaluates security implications, generates structured JSON schemas, writes ready-to-use Terraform and CloudFormation templates, and publishes daily executive digests directly to this site.
Core Capabilities
Comprehensive Security Analysis
Analyzes encryption at rest (KMS, CMK, key rotation), encryption in transit (TLS 1.2/1.3, HTTPS, PrivateLink/VPC endpoints), IAM least-privilege scoping, and monitoring/logging integration.
Automated IaC Template Synthesis
Generates production-grade, hardened Terraform HCL and AWS CloudFormation YAML templates for every analyzed service, embedding security guardrails by default.
Terraform Version Compatibility
Validates and tracks Terraform provider version support, documenting initial availability, latest version compatibility, and linking directly to official registry documentation.
GitOps & Automated CI/CD
Uses PyGithub to commit generated datasets directly into the repository. A GitHub Actions workflow builds and deploys updated static assets to S3 and triggers CloudFront CDN invalidations.
Self-Optimizing Batch Engine
Maintains runtime metrics in AWS Systems Manager (SSM) Parameter Store to dynamically adjust batch sizes (3–5 items) and guarantee completion within the 290s Lambda timeout window.
Zero-Trust Secrets Management
Fetches API keys and GitHub personal access tokens dynamically from AWS Secrets Manager at execution time, ensuring no credentials are ever persisted in code or containers.
Autonomous Architecture & Data Pipeline
The solution is entirely serverless, containerized with Docker on Amazon ECR, and orchestrated with Amazon EventBridge across 4 distinct pipeline stages:
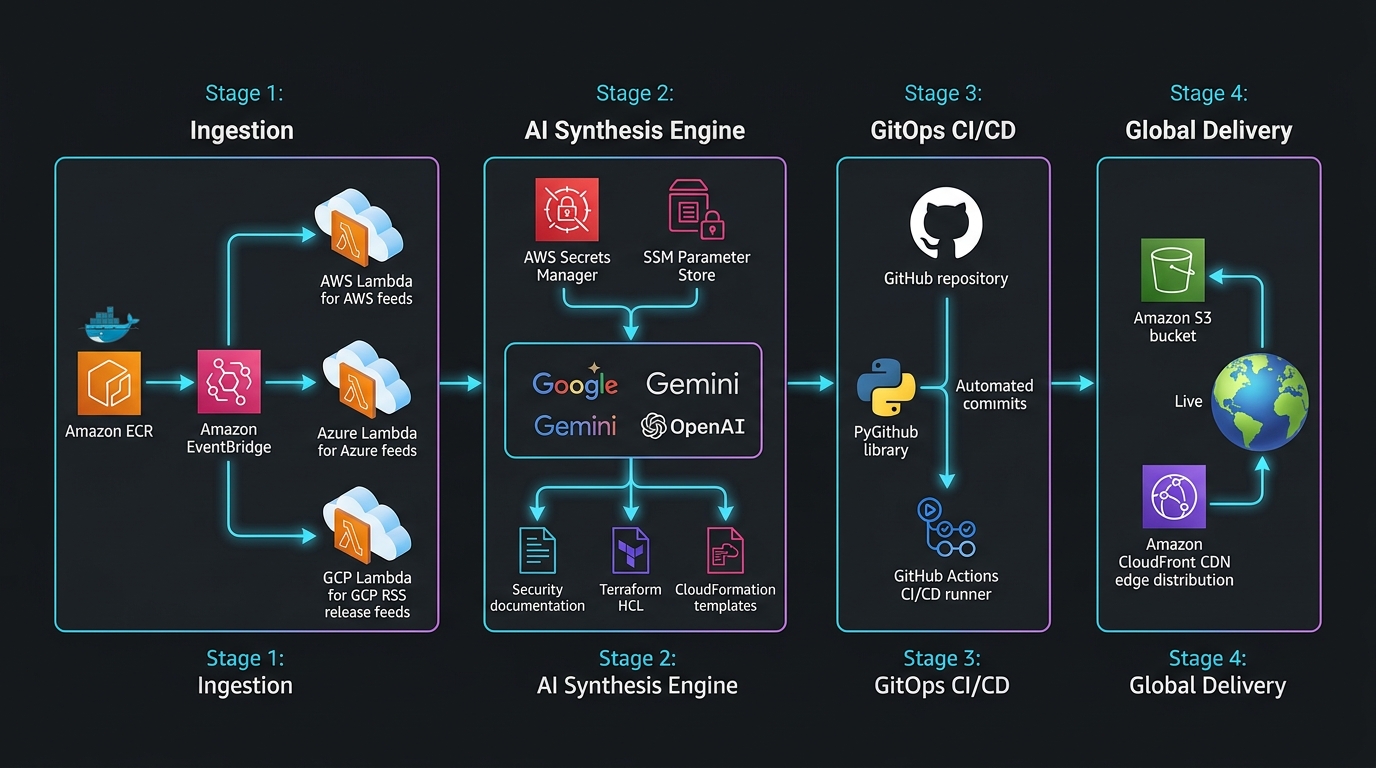
Stage 1: Ingestion
Amazon EventBridge triggers 3 Docker Lambda containers on ECR nightly. Functions parse official AWS, Azure, and GCP RSS feeds and deduplicate entries using processed_urls.json.
Stage 2: AI Synthesis
Retrieves API keys from Secrets Manager and runtime pacing from SSM. Invokes Gemini & OpenAI with strict JSON schemas to generate security analysis, Terraform HCL, and CloudFormation.
Stage 3: GitOps CI/CD
PyGithub writes daily executive digests and service JSON files to GitHub. The push event triggers GitHub Actions runners to build, test, and package the static site assets.
Stage 4: Global Delivery
Syncs static assets to the Amazon S3 origin and issues an instant cache invalidation across the Amazon CloudFront global edge network, delivering fresh daily analysis globally.
Technology Stack
Explore AWS Security Blog Explore Open Source Tools Back to Home